All Categories
Featured
How to Implement Scalable IT Management Policies
Small services should focus on three top priorities: establishing clear ownership of IT decisions (even if someone holds several roles), securing delicate data through basic security controls and compliance checks, and aligning innovation costs with business plan. A light-weight variation of COBIT or the ISO/IEC 38500 standard for business governance of IT provides a beneficial starting structure without requiring a large dedicated team.
Reliable IT governance is not a regulatory problem - it is a competitive lever. Organizations that execute it well make faster, better-informed technology decisions, safeguard themselves from pricey danger occasions, and extract more worth from every IT investment. The five-step technique detailed here - assess, specify authority, pick a structure, build a roadmap, and determine outcomes - supplies a useful course from intent to execution.
Whether your company is building an IT governance plan from scratch or reinforcing an existing structure, the structure is the exact same: clear responsibility, the right framework, and a commitment to continuous enhancement. Frequently asked question What is an IT governance execution strategy?+An IT governance execution plan is a structured roadmap that specifies the policies, roles, decision-making processes, and structures a company will utilize to align IT operations with business technique.
What are the best IT governance frameworks to carry out?+The most commonly adopted IT governance frameworks are COBIT (Control Goals for Info and Related Innovation), ITIL (Information Innovation Infrastructure Library), ISO/IEC 38500 for business governance of IT, and CMMI (Ability Maturity Model Combination). The right option depends on your organization's size, market, threat profile, and existing processes.

Latest Posts
Streamlining Resource Allocation Across Enterprise Systems
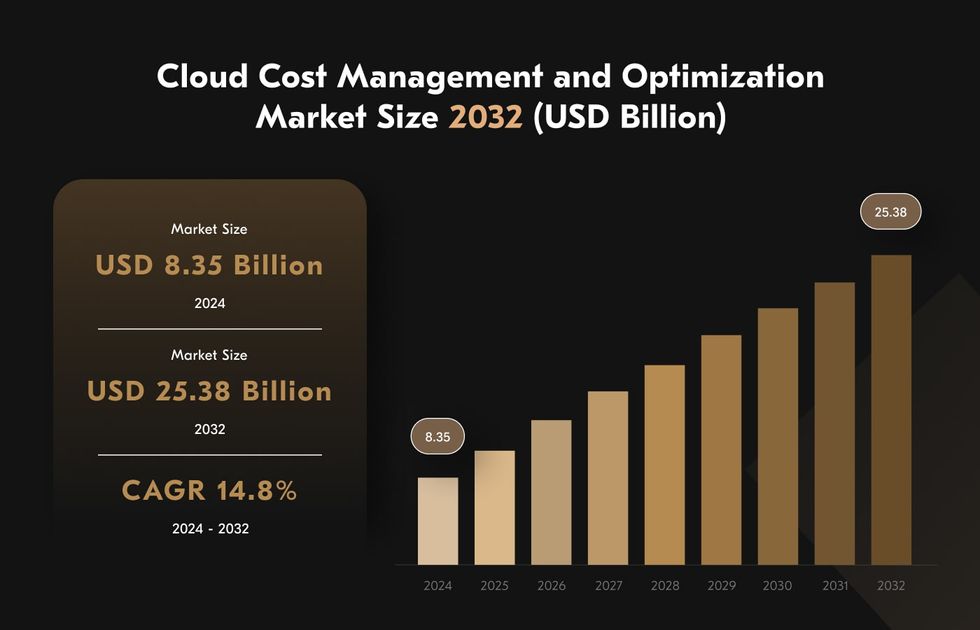
Why Should Cloud Governance Drive Next-Gen ROI?
Maximizing Enterprise Efficiency Through Strategic Governance